Bjorn (infinition/Bjorn) is an open-source, Tamagotchi-style network auditing project built around a Raspberry Pi and an e-Paper display. It can make a controlled security experiment engaging, but its automated actions deserve more preparation than an ordinary device inventory tool. This article explains what the project does, which hardware and software its documentation describes, and how to turn lab observations into useful defensive changes.
What Is Bjorn and Why Does It Exist?
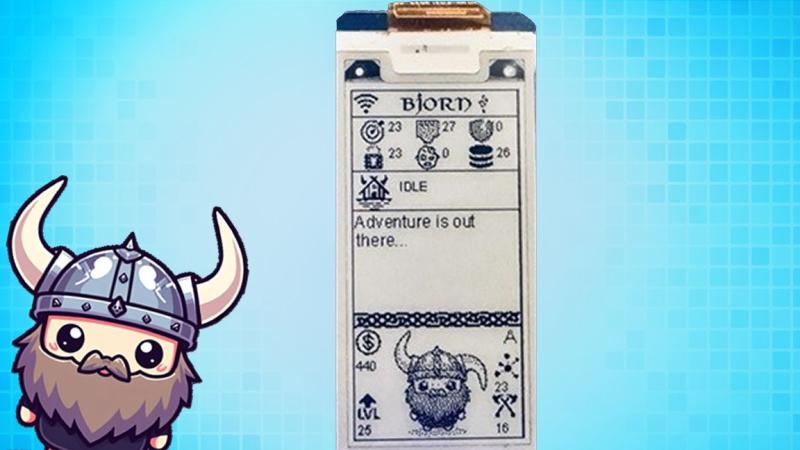
Published by GitHub developer infinition, Bjorn is a portable, open-source offensive security and network auditing tool displayed as a Viking character on a 2.13-inch Waveshare e-Paper screen. Bjorn operates once connected to a local network, using its configured network connection to discover hosts and run selected auditing actions. It is an active testing tool rather than a passive intrusion detector.
Network security tools like Bjorn exist because modern home and small-business networks frequently accumulate forgotten services—such as an old NAS with anonymous SMB shares enabled, a Raspberry Pi with default SSH credentials, or an unpatched database port exposed to the LAN.
What Bjorn Does on an Authorized Lab Network
- Autonomous Subnet Discovery: Uses network scanning to identify live hosts and exposed services; the observed inventory depends on the configured scan and reachable network.
- Service & Credential Auditing: Tests exposed services (such as SSH, SMB, FTP, Telnet, RDP, and SQL ports) against configurable wordlists to detect weak or default passwords on your own lab machines.
- Vulnerability Checks: The project includes Nmap-based vulnerability actions. Findings are leads to investigate against the installed build and vendor advisory; they are not a guarantee that every weakness will be detected or that a reported issue is exploitable.
- e-Paper & Web Dashboard: Shows scan status, discovered hosts and activity through the display and a web interface that starts on port
8000. Check startup logs if that port is occupied; the web code can try a subsequent port.
The Ethical Imperative: Authorized Lab Testing Only
Important Legal & Ethical Notice: Bjorn performs active port scanning, service enumeration, and credential auditing. Run it only within a clearly authorized test scope. Owning an access point does not authorize testing every guest's device. For a first experiment, use an isolated lab containing systems you control and have agreed to test.
Hardware Requirements & How to Set Up Bjorn
To build a dedicated portable Bjorn unit, you only need a few compact components:
- Board and OS: The original Pi Zero W needs a compatible 32-bit image. The documentation names Raspberry Pi OS Lite Bookworm images dated 22 October 2024, with a 6.6 kernel, and community-reported Zero 2 W use of the 64-bit image. This is the project’s documented test baseline, not confirmation that the latest OS release or any ARM board works. Match the board architecture and installer prerequisites.
- Display: The documented setup uses a Waveshare 2.13-inch e-Paper HAT. The project identifies v2 and v4 as tested; verify other revisions before buying rather than assuming every selectable driver was tested.
- Storage: A spare microSD card with room for the chosen OS, installed dependencies and retained results. Keep a clean recovery image separately.
Step-by-Step Installation on Raspberry Pi OS Lite
- Flash Raspberry Pi OS Lite: Use Raspberry Pi Imager to flash an OS Lite image compatible with the exact board, pre-configuring the isolated lab's Wi-Fi and SSH access. Follow the install guide's username and hostname prerequisites; the documented setup uses
bjorn. - Enable SPI & I2C Interfaces: Run
sudo raspi-config, navigate to Interface Options, and enable SPI and I2C so the Raspberry Pi can communicate with the Waveshare e-Paper HAT. - Clone and Inspect the Official Installer: Log in as the documented
bjornuser and work in its home directory. Downloading the repository does not run the installer:
Record the commit outside this directory and inspectsudo apt update && sudo apt install -y git cd /home/bjorn git clone https://github.com/infinition/Bjorn.git cd Bjorn git rev-parse HEADinstall_bjorn.shbefore proceeding. The full installer changes system settings and enables automatic startup; it does not offer the optional-autostart choice of an ordinary desktop application. When its prerequisites and changes suit this disposable lab installation, run:
Select the correct display revision and follow the documented reboot requirement. Review compatibility warnings rather than skipping failures until the installer reports completion.chmod +x install_bjorn.sh sudo ./install_bjorn.sh - Access the Web Control UI: Use the Pi's actual private address on port
8000, as described in the installation guide. Review the running configuration and action modules before connecting the unit to any wider network; do not infer that a device-discovery setting disables every offensive action.
Practical Homelab Use Cases for Bjorn
- Reviewing a Disposable IoT Lab: Check approved test devices for unexpected Telnet, FTP or web listeners. An open HTTP port alone does not tell you whether its management page requires authentication; verify the service separately within the permitted scope.
- Testing Intrusion Detection Alerts: If you've just deployed CrowdSec, Fail2ban, or Suricata in your homelab, an explicitly scoped lab exercise can test the alerts those tools are configured to produce. A host-discovery notification from NetAlertX is different from an IDS detecting a scan or Fail2ban observing failed authentication.
- Checking New Lab Systems: Use agreed tests against disposable VMs or containers to investigate an unnecessary listener or weak synthetic account, then document the fix. Do not assume a scan proves all credentials or shares are safe.
Start with an Inventory Question, Not Unattended Automation
The project repository describes more than discovery: it includes credential-attack and file-extraction actions. That makes configuration review central to a useful experiment. The educational goal might be finding an unnecessary service on a disposable VM, not exercising every action against a network of daily-use devices.
Write down the test subnet, permitted hosts, allowed actions, start time and stopping condition. Use synthetic accounts and sample files. Keep the lab apart from work computers, family devices, backups and any network where guests are connected. Check that its routing rules actually enforce that separation; an SSID with a different name is not enough.
Follow the documented prerequisites and review the installer itself. It installs Python dependencies system-wide using --break-system-packages, adjusts system limits and PAM, configures USB gadget networking and creates a service running as root. It also removes Git metadata at the end, which is why recording the revision beforehand matters. Keep the unit on its isolated lab network through reboot and configuration review; installation completion does not mean its action scope is appropriate.
Turn Findings into Fixes
| Observation in a lab | Question to answer | Useful next action |
|---|---|---|
| A previously unknown host | Who owns it, and should it be in this segment? | Compare the router inventory and assign a documented owner |
| An unexpected listening service | Is the service required from this source network? | Disable it or restrict the approved access path |
| A version or vulnerability indication | Does the installed build actually match the affected product? | Verify with the vendor advisory before planning remediation |
| A missing expected alert | Was the relevant detector enabled and able to see the event? | Check the event source and notification delivery separately |
An open port is not proof of a vulnerability. It shows that a service answered within the scope of that observation. Confirm the service's purpose and supported version, apply the relevant update or rule change, and repeat the same approved check. Record the result rather than measuring success by the number of dramatic findings on the display.
Protect the Audit Device and Its Results
Keep the management interface private and protect access to its storage. The current web server code binds to available interfaces and exposes configuration, result downloads and actions without a login check in that handler. Treat access to it as administrator access to the test unit. Do not place it on a guest or shared management network. Inventory records and results can reveal network details; use synthetic data and avoid publishing raw output.
The default configuration includes automatic mode, retries, a port list and example exclusion addresses. Review those actual values and the action modules; example exclusions are not your own scope policy. Disconnect the unit when testing finishes. On the unit itself, stop and disable the documented service so it does not resume after another reboot:
sudo systemctl disable --now bjorn.service
sudo systemctl status bjorn.service --no-pager
sudo journalctl -u bjorn.service -n 50 --no-pager
A disabled service may remain listed in the status output; verify it is inactive. Stopping it does not undo package, boot or host-network changes. For a clean recovery, shut down the Pi and restore the spare card image rather than assuming rerunning the installer reverses its changes.
When troubleshooting, separate display problems from network problems. A mismatched e-paper driver can leave the screen blank while a service is still running; a successful UI connection does not prove the intended subnet was scanned. Check the board revision, installer logs under /var/log/bjorn_install, assigned IP and actual test scope independently. The troubleshooting guide also identifies a partially resolved long-runtime file-descriptor issue. Investigate repeated service restarts instead of treating them as proof of reliable unattended operation. Finish by disconnecting the test unit and reviewing the changes needed on the lab hosts.
Pros and Cons of Bjorn
Pros
- Automated Lab Workflows: Can repeat configured discovery and actions, provided scope and results are supervised.
- Compact Hardware: Uses compact Raspberry Pi hardware; actual power use depends on the board, wireless activity and peripherals. Measure your own complete setup if runtime matters.
- Open-Source & Extensible: Written in Python, with configurable scanning intervals, wordlists and action modules; extending it still requires understanding the code and test scope.
Cons
- Disruptive Active Checks: Scans and credential checks can generate logs, account lockouts and defensive bans. Keep ordinary production systems outside the experiment rather than disabling their protections to accommodate the tool.
- Strict Authorization Required: Never carry an auto-connecting Bjorn unit onto public, workplace, or third-party Wi-Fi networks.
Conclusion
When used responsibly inside your own homelab, Bjorn turns an inexpensive Raspberry Pi Zero and e-Paper display into an engaging, educational red-team companion. By showing you your network through the eyes of an automated scanner, it can help you investigate unnecessary services, strengthen lab credentials and check specific defensive alerts. Those benefits depend on corroborating findings and making the corresponding changes.
Visit the official Bjorn repository on GitHub or explore our other Network & Homelab Security guides.